The Proofline
Trusted AI. Industrial autonomy. The evidence in between.
Editorial review · 1 October 2026

Tomorrow’s autonomy.
Today’s evidence questions.
What supports the machine’s recommendation—and what still needs checking?
Follow the developments. Inspect the sources. Leave with a question your team can use.
What would you like
to understand better?
Choose a path, examine a small example, then take a practical next step. No records to upload. No account needed for the experience.
2 of 3 · Inspect the support
Prepared fictional example · no real-case processing or operational decision
Your learning takeaway
Read the development.
Inspect what supports it.
Original summaries with primary sources, practical relevance and an explicit open question. Global describes our coverage—not offices, deployments or partnerships.
8 briefings
No matching briefings
Try a broader term or use Clear filters to see the full selection.
A new OT-security draft puts asset context in focus.
NIST’s new operational-technology security draft expands guidance on asset management, monitoring and security architecture. Public comments are due 30 November 2026.
Statement: OT-security guidance must consider performance, reliability and safety requirements.
Primary source: NIST — Guide to Operational Technology Security, Revision 4 draft
Date / version: 21 September 2026 · SP 800-82 Rev. 4 ipd
Supporting passage:
“performance, reliability, and safety requirements”
Qualification: NIST’s scope is operational-technology security. The connection to our proposed evidence workflow is editorial interpretation, not conformity or endorsement.
What changed
NIST’s new operational-technology security draft expands guidance on asset management, monitoring and security architecture. Public comments are due 30 November 2026.
Why it matters
Our practical question for edge-connected industrial assets: does the review record identify the equipment, configuration and context that the claim concerns?
How we are responding
The developing Mission Evidence approach keeps those questions attached to an example handoff. Evidence organization complements the work of qualified security and engineering teams.
What remains open
This is a draft, not a new mandatory standard. The webpage does not implement security controls, protect a network, or validate an autonomous system.
Your next question: Ask which asset version, operating conditions and security assessment support the decision.
AI-assisted reporting still needs a human evidence check.
NIST has published a draft guide for using AI in Cybersecurity Framework analysis and reporting. The comment deadline is 15 October 2026.
Statement: NIST’s examples are not prescriptive assurance methodologies.
Primary source: NIST SP 1353 — Initial Public Draft
Date / version: 19 August 2026 · SP 1353 ipd
Supporting passage:
“not prescriptive assessment or assurance methodologies”
Qualification: This qualification belongs to NIST’s illustrative use cases. Our demonstration is independently prepared and is not a NIST implementation.
What changed
NIST has published a draft guide for using AI in Cybersecurity Framework analysis and reporting. The comment deadline is 15 October 2026.
Why it matters
A generated profile can look complete while assumptions and evidence gaps remain. Review the inputs and the reasoning behind each reported outcome.
How we are responding
Our editorial response is to make the source and its limits inspectable. The fictional example below shows how one missing context detail changes a conclusion.
What remains open
This is draft guidance, not a prescriptive assessment method or an endorsement of our products. An organized record does not establish cybersecurity effectiveness.
Your next question: Compare a reported outcome with the actual record supporting it.
Critical infrastructure needs requirements that survive a handoff.
NIST is developing an AI risk-management profile for critical infrastructure and has established a community of interest.
Statement: The critical-infrastructure profile is an ongoing development project.
Primary source: NIST — Trustworthy AI in Critical Infrastructure Profile concept note
Date / version: 6 April 2026 (page creation) · Concept note / ongoing profile project
Supporting passage:
“Project Status”
Qualification: The source labels its project status “Ongoing.” A concept note is not a final sector standard.
What changed
NIST is developing an AI risk-management profile for critical infrastructure and has established a community of interest.
Why it matters
Operators need to communicate requirements across suppliers, models and changing asset configurations. A generic trust claim leaves the operating context unclear.
How we are responding
Mission Evidence explores a reviewable handoff: asset context, source versions, unresolved questions and a responsible reviewer.
What remains open
The profile is being developed. We make no claim of NIST participation, approval or conformity. Our proposed workflow is not an operational safety process.
Your next question: Name the asset, operating context and owner of each requirement.
Ask what the standard covers before asking who complies.
ISO/IEC 42001 sets requirements for an organizational AI management system.
Statement: ISO/IEC 42001 addresses an AI management system within an organization.
Primary source: ISO — ISO/IEC 42001:2023 overview
Date / version: December 2023 · ISO/IEC 42001:2023, edition 1
Supporting passage:
“Artificial Intelligence Management System (AIMS) within organizations”
Qualification: This overview does not establish that The Truth Calculator or any developing offering conforms to the standard.
What changed
ISO/IEC 42001 sets requirements for an organizational AI management system.
Why it matters
A management system concerns policies and processes. That scope is different from proving a particular robot, prediction or component is safe for its intended use.
How we are responding
We explain the source’s scope before connecting it to an evidence-review question. This page makes no certification or conformity claim.
What remains open
The public overview was reviewed; the paid standard was not purchased or audited. Technical testing, operational authorization and applicable law need separate assessment.
Your next question: Ask for the exact standard, edition, assessed scope and supporting evidence.
AI obligations depend on the use, the role and the applicable date.
The Commission’s current overview distinguishes risk-based AI rules and staged application, with exceptions to general applicability.
Statement: The AI Act’s application has exceptions and depends on the relevant provisions.
Primary source: European Commission — AI Act overview
Date / version: AI Act entered into force 1 August 2024 · Commission overview of Regulation (EU) 2024/1689 and subsequent changes
Supporting passage:
“with some exceptions”
Qualification: See the Commission’s application timeline and linked legislation. This page deliberately does not turn a general overview into a checklist for your system.
What changed
The Commission’s current overview distinguishes risk-based AI rules and staged application, with exceptions to general applicability.
Why it matters
An operator, provider or integrator must identify its actual role and use case before treating a requirement as applicable.
How we are responding
Our educational approach keeps jurisdiction, source date and qualification beside a statement, and leaves applicability questions visible.
What remains open
This briefing is not a compliance assessment or legal advice. Use the official text and qualified advice for the current rules and deadlines applying to a specific activity.
Your next question: Record the jurisdiction, organizational role and specific provision needing review.
A test result needs the machine and conditions it actually tested.
NIST’s program describes measurement work covering both robotic components and integrated systems, with application context informing performance requirements.
Statement: Robotic performance includes both components and the integrated system.
Primary source: NIST — Measurement Science for Robotics and Autonomous Systems
Date / version: 11 December 2018 (page creation) · Current program overview
Supporting passage:
“as an integrated system”
Qualification: This is a research-program description, not certification of a product or validation of our fictional equipment.
What changed
NIST’s program describes measurement work covering both robotic components and integrated systems, with application context informing performance requirements.
Why it matters
A result from one configuration or environment cannot automatically answer a different operational question.
How we are responding
Our prepared maintenance example lets a reader question a reference after a component change, while retaining the original alert.
What remains open
The example does not measure a real robot, validate a model, or authorize maintenance. Physical safety, cybersecurity and performance each need their own evidence.
Your next question: Check configuration, environment, test method, limits and reviewer responsibility.
AI assurance needs skills as well as records.
The UK roadmap sets out ambitions for the assurance market, including professional skills and government support for its development.
Statement: This document sets out government ambitions for the assurance market.
Primary source: DSIT — Trusted third-party AI assurance roadmap
Date / version: 3 September 2025 · 2025 policy roadmap
Supporting passage:
“ambitions for the third-party assurance market”
Qualification: The source is a policy paper. Its ambitions should not be presented as an already completed professional or accreditation system.
What changed
The UK roadmap sets out ambitions for the assurance market, including professional skills and government support for its development.
Why it matters
Having a file is different from having a qualified person evaluate the evidence and explain its limits.
How we are responding
We retain the human-review boundary and a place for the responsible reviewer in our example evidence receipts.
What remains open
A roadmap is not a universal certification scheme. We make no claim of participation, accreditation or government endorsement.
Your next question: Agree the review question, reviewer competence and acceptance criteria.
Experience the evidence question before discussing an integration.
The public Mission Evidence page contains a guided fictional maintenance investigation and an example receipt. This is a verifiable website experience.
Statement: The Mission Evidence experience is a prepared fictional demonstration.
Primary source: The Truth Calculator — Mission Evidence and current product pages
Date / version: Underlying page publication date not stated · Public Mission Evidence experience
Supporting passage:
“Prepared fictional demonstration”
Qualification: The public page identifies the example as fictional. It neither processes real operational records nor grants maintenance approval.
What changed
The public Mission Evidence page contains a guided fictional maintenance investigation and an example receipt. This is a verifiable website experience.
Why it matters
Teams can explore the evidence-review idea before discussing a bounded evaluation.
How we are responding
The developing xOSYSTEM connects individual, investigative and organizational use concepts. The role map below separates these plans from availability.
What remains open
A web demonstration is not a released integrated suite, SDK, predictive model, customer deployment or production integration. Pricing and availability are not established by this example.
Your next question: Start with one asset context, one evidence question and synthetic examples.
Editorial selection checked 1 October 2026. This is a dated briefing edition, not a live news feed. Sources and status must be checked again before acting.
Different sources.
Different kinds of authority.
There is no single universal “Trusted AI Autonomy standard.” Ask what a source is, where it applies and what it actually establishes.
Voluntary framework
NIST AI RMF 1.0
Risk-management guidance; released 26 January 2023. NIST reports revision work underway.
Published standard
ISO/IEC 42001:2023
An organizational management-system standard. Exact scope matters.
Enacted legislation
EU AI Act
Rules with staged application and use-specific obligations.
Draft or roadmap
NIST SP 1353 draft and UK assurance roadmap
Development and policy direction must retain their qualifications.
Evidence records address part of the trust problem. Equipment safety, cybersecurity, model performance and operational authorization require their own evidence and processes. No standard, authority or legislation is represented as mandating or endorsing our products.
One evidence question.
Several developing pathways.
Explore the roles without mistaking a roadmap for a released suite. Status checked against current public product pages on 1 October 2026.
The Truth Calculator™
An individual starting point for examining claims and supporting records.
Preparing for releaseAdveriTrace™
A planned deeper investigation and review-draft pathway.
Planned upgradeMission Evidence
An organizational evidence-receipt concept for qualified review.
Proposed pathway · web demo availableqX-TGRI™
The developing evidence-review engine concept.
In developmentxBITTY™
A developing specialist solution family.
In developmentqX Alliance™
The commercial and partner framework associated with BEYONDx.
Framework · no partnership impliedxOSYSTEM™
The wider developing ecosystem connecting these directions.
Developing ecosystemNo verified App Store listing is linked in this edition. No purchase, production SDK, deployed integration or validated predictive performance is offered by this page.
Planning context and preserved product boundaries
The previous Newsroom status record described Build 8 evidence and the Rev G product boundary, a qualified November 2026 Forensic target dependent on Base v1.0 readiness and ten open gates, price TBD and no release approval. It also described seven further planned paid modules within an eight-module planning model, superseding an earlier twenty-path concept. These are historical planning references, not current release commitments. No new release approval has been verified for this edition.
The qX Evidence Receipt Schema v0.1 remains a draft concept, not an adopted industry standard. qX-TGRI™ is left unexpanded pending formal naming resolution. Detailed internal build evidence is not linked publicly.
BEYONDx Advisors is the commercial sponsor, product operator, advisory company and controlled IP steward identified in the existing Newsroom record. Qualified human review remains essential. Evidence review does not authenticate evidence, determine legal liability, certify compliance or guarantee admissibility.
Any Moon or Mars discussion is a future concept, not a deployment or partnership. Real operational records require appropriate rights, qualification, written authorization and a separately agreed scope.
The original record
stays on the record.
Original articles, dates and attribution remain at their existing URLs. Historical plans should be read beside the current product-status information above.
New Counter-Drone Rules Raise the Bar for Mission Evidence. The Truth Calculator Outlines Its Response.
Planned mission-evidence workflows, source authority and human review.
BEYONDx Advisors Unveils The Truth Calculator™ Roadmap for Evidence-Ready Decisions in the Age of AI
The dated roadmap announcement remains available with its original attribution.
The Truth Calculator™ Is Not Another AI Chatbot—It Checks Whether the Answer Has Receipts
The original explanation of the evidence-readiness idea and supporting receipts.
Media resources and editorial practice
Use the linked original announcements for attributable company statements. For a current quote, approved press image, product-status confirmation or correction, use the existing BEYONDx contact route. No new press quotation or downloadable media license is implied by this page.
Our briefing format separates the external development, our interpretation, our stated response and the unresolved question. Source publication dates and editorial review dates are shown separately. Substantive corrections should explain what changed and retain the prior record.
Illustrations and fictional examples teach a question; they do not document an actual customer or field test. Source links go to public material. Internal implementation and QA records stay outside the public media area.
Bring one evidence question.
Define a bounded next step.
For a B2B discussion, start with one asset context, one question and synthetic examples. Agree the review criteria before considering real operational records.
Start with non-confidential information. Scope, availability, responsibilities and terms are agreed separately. This page makes no maintenance approval, safety, legal or compliance determination.
© 2026 BEYONDx Advisors, LLC. All rights reserved. Sources retain their respective rights.
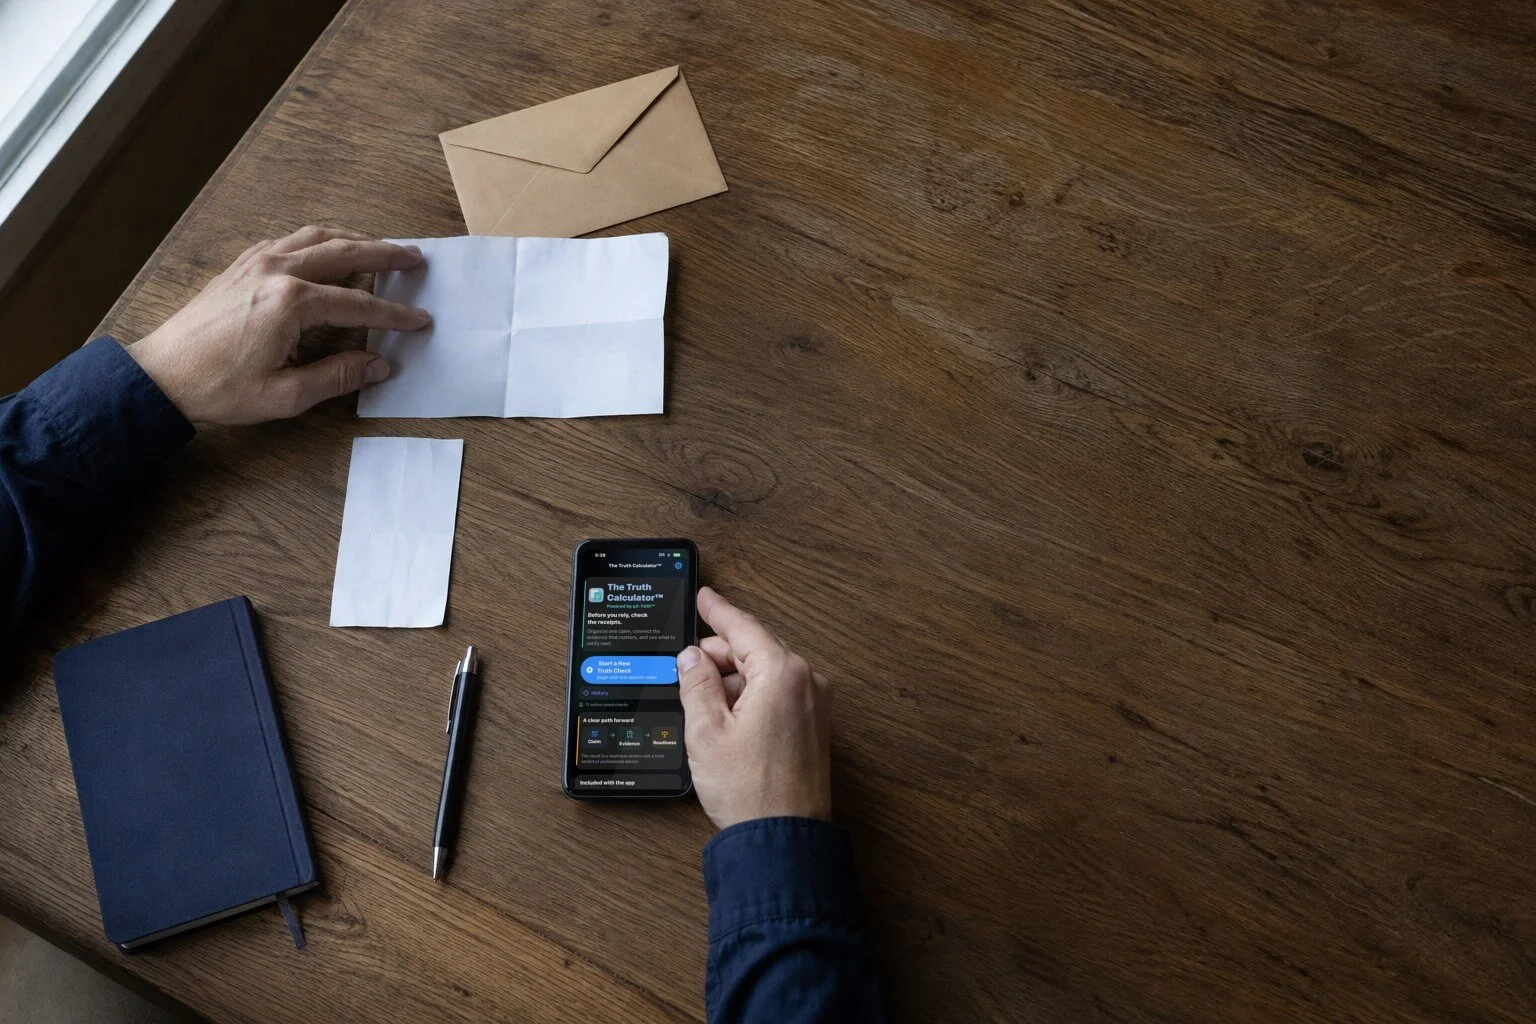
The Truth Calculator™ Is Not Another AI Chatbot—It Checks Whether the Answer Has Receipts
The Truth Calculator™ is a patent-pending evidence-readiness system designed to check claims against source material and show supporting receipts, conflicts, and missing evidence—without pretending software can manufacture certainty.